A Practical Account Security Checklist for Everyday Users
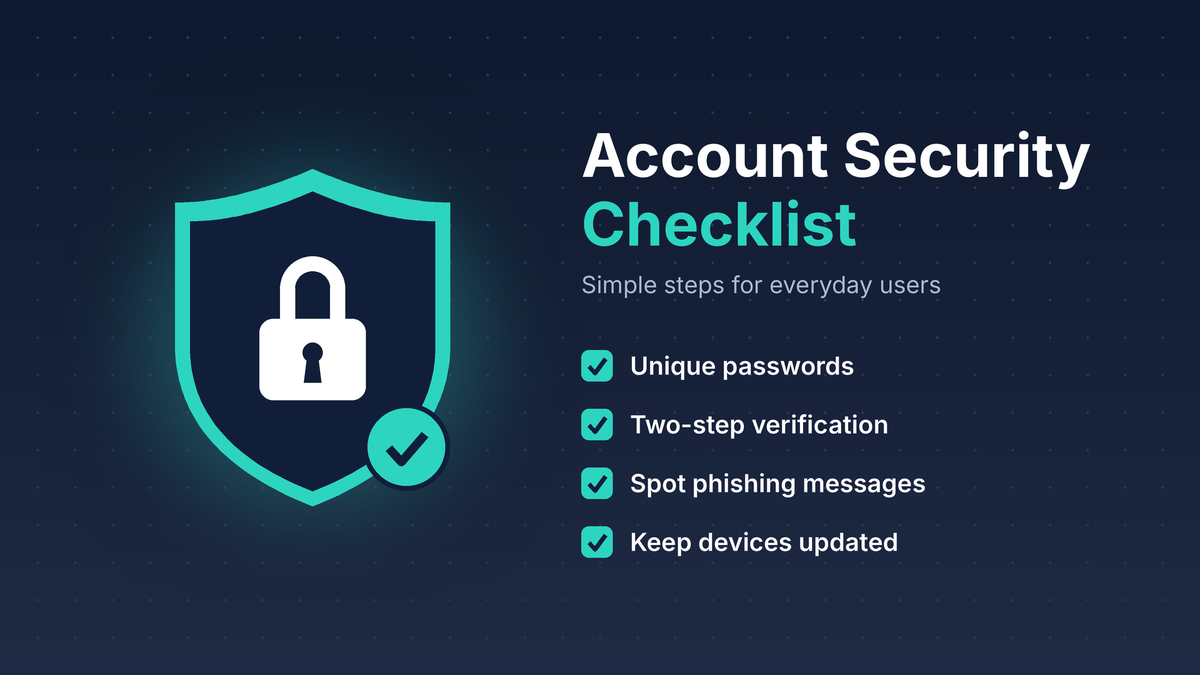
Simple steps you can take this week to protect your email, bank, and social media accounts
October is Cybersecurity Awareness Month, which seems like a good time to write about something that is not flashy but matters a great deal: protecting your online accounts.
Through my OSINT work, I have seen how often a reused password, a forgotten account, or an email address with no second layer of protection becomes the starting point for a much bigger problem. Most account takeovers are not sophisticated. They take advantage of habits we all have when we are busy.
The good news is that you do not need to be technical to make a real difference. This is the checklist I would walk a family member through. You do not have to finish it in one sitting. Start at the top and work your way down.
1. Start with your email account
Your email account is the master key to everything else, because most password resets are sent there. If someone gets into your email, they can often get into your bank, your shopping accounts, and your social media.
- Use a long, unique password that you do not use anywhere else.
- Turn on two-step verification (more on that below).
- Confirm that the recovery phone number and backup email address are current and still belong to you.
- Review the list of devices signed in to your account and sign out any you do not recognize.
- Check your forwarding and filter settings. Attackers sometimes quietly forward copies of your mail to themselves.
2. Use a password manager
I would not ask anyone to remember dozens of long, unique passwords. A password manager creates them, stores them, and fills them in when you need them. CISA recommends using one for exactly this reason. (cisa.gov)
- Choose a reputable manager. I would rather see someone use the one built into their phone or browser than keep reusing the same password.
- Protect the manager itself with a long passphrase you have never used anywhere else, and turn on two-step verification for it.
- Start with the accounts that matter most: email, banking, your phone carrier, your Apple, Google, or Microsoft account, and social media.
- Replace weak and reused passwords as you go. You do not have to fix them all at once.
3. Choose length over complexity
For the passwords you do have to remember, such as your password manager and your device logins, longer is better than clever. NIST’s current guidance puts the emphasis on length rather than complexity rules, and it no longer recommends forcing regular password changes unless there is evidence of a compromise. (malwarebytes.com)
A passphrase made of several unrelated words is easier to remember and harder to guess than a short string of symbols. I would avoid anything tied to personal details, such as birthdays, pet names, or the names of children and grandchildren. That information is often easy to find on public profiles.
Change a password when you have a reason to, such as a breach notice or a suspicious sign-in, rather than because a calendar says so.
4. Turn on multifactor authentication
Multifactor authentication, also called two-step verification or two-factor authentication, adds a second check beyond your password. Even if a criminal gets your password, they still cannot sign in without that second factor. (cisa.gov)
Not all second factors are equal. In general, I would choose them in this order:
- Passkeys or a physical security key. CISA recommends passwordless sign-in, such as passkeys, whenever it is available. (cisa.gov)
- An authenticator app that generates codes on your phone.
- Text message codes. These are the weakest of the three, but still far better than nothing.
Start with your email, financial accounts, social media, cloud storage, and your phone carrier account. Save the backup codes the service gives you and keep them somewhere safe. Never read a verification code to anyone who contacts you. A real company will not ask for it.
5. Slow down on suspicious messages
The FTC explains that scammers use emails, texts, and even phone calls to get your login details and other personal information. They often pretend to be a company you know and tell a story, such as a problem with your account or suspicious activity, to get you to click. (consumer.ftc.gov)
Here is what I do:
- Treat urgency as a warning sign. A message that demands you act right now deserves extra scrutiny.
- Do not click links or open attachments in unexpected messages. Go to the website directly or use the company’s official app.
- If a message claims to be from your bank, call the number on the back of your card.
- Be careful with QR codes and links sent by text, even from numbers that look familiar.
- Report scams at reportfraud.ftc.gov.
If you do click and enter your password, change it right away, change it anywhere else you used it, and make sure two-step verification is turned on.
6. Check whether your information has been exposed
Data breaches happen constantly, and your email address has probably been in at least one. Have I Been Pwned lets you check an email address against known breaches. I built a small tool around it, which I wrote about in PwnedLookup Tool, but the original site works well on its own. If your address shows up, change the password for that service and anywhere else you used the same one.
7. Clean up old accounts and connections
Every account you no longer use is one more place for your information to leak from.
- Close accounts and subscriptions you do not use anymore.
- Review the apps and websites connected to your Google, Apple, Microsoft, and Facebook accounts and remove the ones you do not recognize or use.
- Remove old devices from your account sign-in lists.
- Delete saved payment cards from sites where you no longer shop.
8. Protect your phone number and keep devices updated
Your phone number is tied to many of your accounts, so I would call your mobile carrier and ask about adding a PIN or port-out protection. That makes it harder for someone to take over your number.
Turn on automatic updates for your phone, computer, browser, and apps. Updates fix known security flaws. Also use a screen lock with a PIN or biometrics on every device.
9. Know what to do if an account is compromised
- Change the password from a device you trust and sign out all other sessions.
- Change the password anywhere else you reused it.
- Check your recovery options and forwarding rules for changes you did not make.
- If money is involved, contact your bank or card issuer right away.
- If personal information such as your Social Security number may be exposed, consider a credit freeze, which is free, and report identity theft at IdentityTheft.gov.
- Warn friends and family if the account was used to message them.
The quick checklist
If you only want the short version, here it is.
☐ My email account has a unique password and two-step verification.
☐ I use a password manager, protected by a long passphrase.
☐ My most important accounts use passkeys or an authenticator app.
☐ My recovery phone numbers and backup email addresses are current.
☐ I checked my email address for breaches and updated passwords where needed.
☐ I know how to spot a phishing message and where to report one.
☐ I removed old accounts and unused app connections.
☐ My mobile carrier account has a PIN or port-out protection.
☐ Automatic updates and screen locks are turned on.
☐ My backup codes are saved in a safe place.
Start with one thing
If this feels like a lot, pick one item and do it today. Securing your email account and turning on two-step verification will do more than almost anything else on this list. Then come back next week and do another.
If you are the person your family calls when something goes wrong with a computer, share this checklist with them. I would much rather have that conversation before a problem than after.
What is the first change you plan to make? I would be interested to hear what has worked for you and your family.